AWS Two-Tier Cloud Infrastructure
AWS Two-Tier Cloud Infrastructure: Automated CI/CD Deployment.
From the brief to the build.
The Challenge
The project was built to demonstrate enterprise-level DevOps and infrastructure automation practices: a production-grade, highly available two-tier architecture on AWS, with the complete cloud environment provisioned through code and deployments fully automated.
The Solution
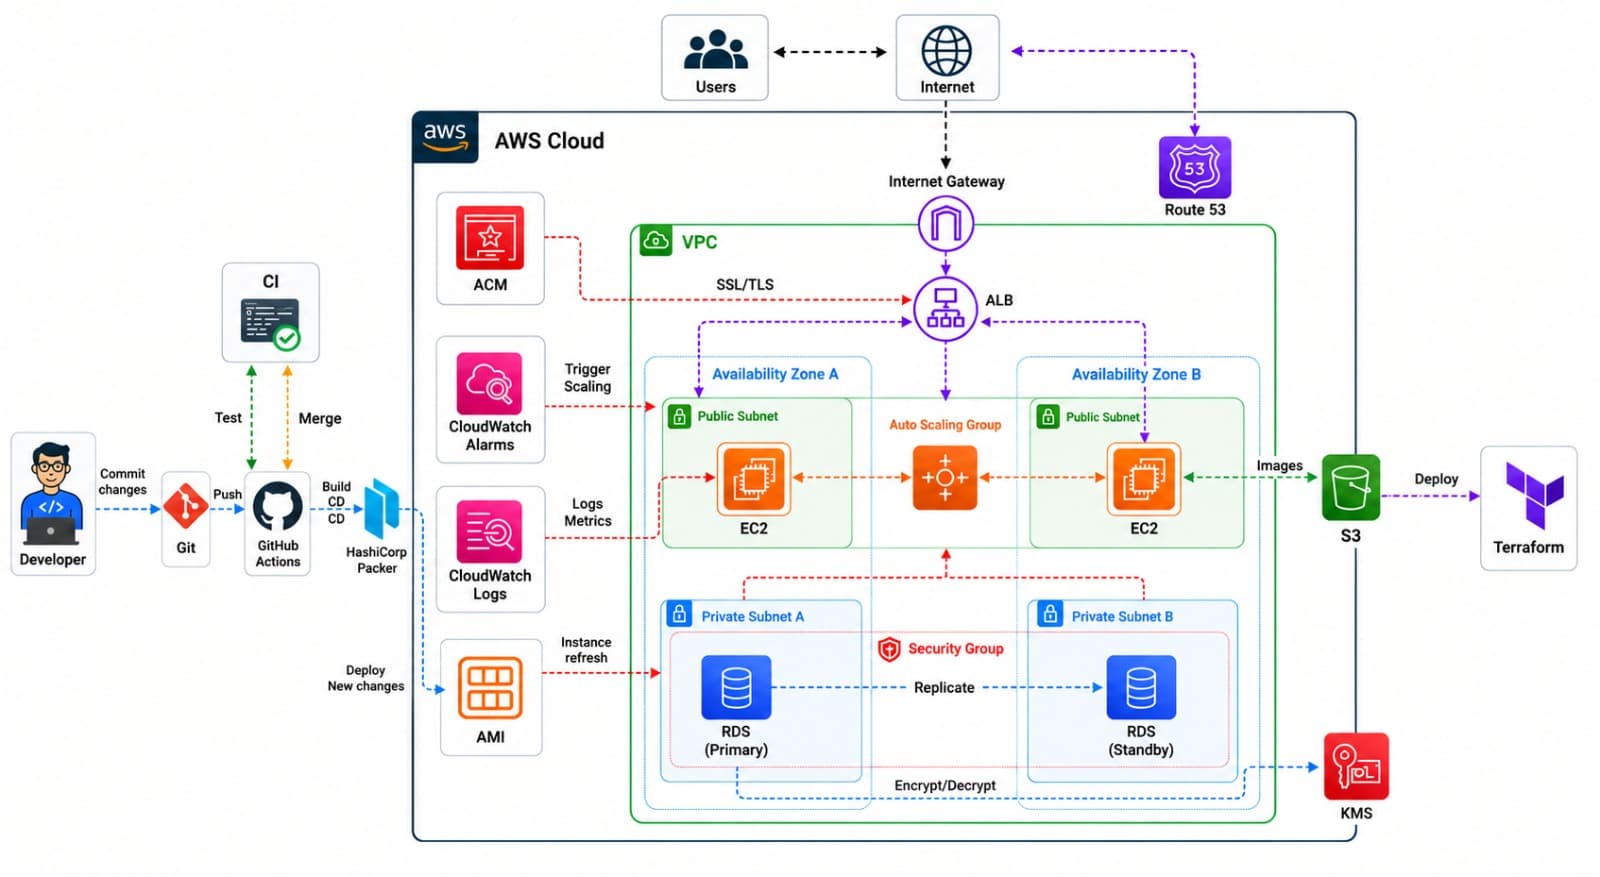
A two-tier architecture deployed on AWS. The environment is defined entirely as Infrastructure as Code using Terraform, application images are baked with Packer, and GitHub Actions orchestrates the CI/CD pipeline from AMI build to instance refresh.
- Type
- In-house product
- Category
- Cloud & Data Engineering
- Services provided
- Cloud infrastructure
- DevOps and CI/CD
- Related service
- Tech stack
- AWS VPCEC2Application Load BalancerRDS PostgreSQLKMSSecrets ManagerCloudWatchTerraformPackerGitHub ActionsNext.jsTypeScript
The pieces that made it work.
Infrastructure as Code
The complete cloud environment is provisioned entirely through Terraform: a VPC with public and private subnets, an Auto Scaling EC2 fleet behind an Application Load Balancer, and a Multi-AZ RDS PostgreSQL database.
Immutable images
Application images are baked with Packer for consistent, immutable deployments.
Automated CI/CD pipeline
GitHub Actions orchestrates a fully automated CI/CD pipeline, from AMI build to zero-downtime instance refresh, secured with GitHub OIDC for keyless, short-lived AWS authentication.
Security and observability
The stack includes KMS encryption, AWS Secrets Manager for credential management, and CloudWatch monitoring for full observability.
Got something like this in mind? Let's build it.
Tell us what you're building — we'll show you how we'd approach it.